Category

Microsoft

Windows, Windows Server, Microsoft 365, Word, Excel, PowerPoint, Outlook, OneNote, Teams, SharePoint, OneDrive, Edge, Bing, SQL Server, Visual Studio, Active Directory, Dynamics 365, Power BI, Power Apps, Xbox, Game Pass, Surface, Intune, Defender, Exchange, Hyper-V, .NET, Dataverse, Microsoft Copilot, Copilot Studio, Microsoft Fabric, Power Platform, Windows 11, Windows 10, WSL, Windows Subsystem for Linux

Page 2
Antino: A Stealthy Backdoor That Hides in Outlook and OneDrive

Antino: A Stealthy Backdoor That Hides in Outlook and OneDrive

A new espionage campaign tracked by Cisco Talos has exposed a sophisticated Windows backdoor, nicknamed Antino, that uses Microsoft 365 services as its covert communications channel. Targeting government and policy organizations across Asia — including Taiwan, India, the Philippines, Cambodia, Pakistan, Thailand, and Myanmar — the activity centers on highly tailored spear‑phishing lures and a multi-stage infection chain that culminates in a Rust-compiled implant communicating through Outlook and OneDrive. The…
Saugata Datta5 min read206
Attackers Exploit SharePoint Authentication Bypass After Public PoC Release

Attackers Exploit SharePoint Authentication Bypass After Public PoC Release

Microsoft’s SharePoint platform is facing active exploitation following the public release of a proof-of-concept (PoC) for a critical authentication bypass vulnerability tracked as CVE-2026-55040. Patched in July’s Patch Tuesday, the flaw allows unauthenticated actors to impersonate SharePoint users by forging JSON Web Tokens (JWTs). Since the PoC surfaced, security researchers and telemetry providers have observed real-world attempts that underscore the urgency for administrators to apply updates and audit their environments.…

Saugata Datta3 min read228
Microsoft Confirms July Windows Update Is Causing Some Dell Laptops to Shut Down and Overheat

Microsoft Confirms July Windows Update Is Causing Some Dell Laptops to Shut Down and Overheat

Microsoft has acknowledged that a recent Windows 11 preview update has caused a limited number of Dell laptops to experience unexpected shutdowns, higher operating temperatures, rapid battery drain, and reduced performance. The issue was first flagged during Dell’s internal testing and later confirmed by Microsoft on July 14, 2026. A specific Intel driver interacting with a newly introduced Windows USB-C Connection Manager appears to be the root cause. The problem…

Saugata Datta3 min read185
Microsoft Extends Windows 10 Extended Security Updates Through October 2027

Microsoft Extends Windows 10 Extended Security Updates Through October 2027

Microsoft has quietly extended its consumer Extended Security Updates (ESU) program for Windows 10, pushing the cutoff for critical security patches out another year to October 12, 2027. The move gives millions of users who have not yet migrated to Windows 11 additional time to receive important and critical security fixes, while Microsoft continues to encourage upgrades to the newer OS. For those already enrolled in the consumer ESU program,…

Saugata Datta3 min read202
Breaking the code: how a multi-stage “code of conduct” phishing campaign led to AiTM token compromise

Breaking the code: how a multi-stage “code of conduct” phishing campaign led to AiTM token compromise

Phishing has evolved from crude scams to carefully engineered deceptions that mimic trusted internal processes. In mid‑April 2026, Microsoft Defender Research observed a large, multi‑stage campaign that did exactly that: it masqueraded as internal “code of conduct” notifications, used polished templates and legitimate delivery services, and funneled victims through a sequence of CAPTCHA and staging pages that ultimately proxied real authentication flows. The result was an adversary‑in‑the‑middle (AiTM) compromise capable…

Saugata Datta6 min read249
Critical Microsoft 365 Copilot Flaws: What Organizations Need to Know

Critical Microsoft 365 Copilot Flaws: What Organizations Need to Know

Microsoft has disclosed and silently remediated three critical information-disclosure vulnerabilities in Microsoft 365 Copilot and Copilot Chat in Microsoft Edge. The flaws—CVE-2026-26129, CVE-2026-26164, and CVE-2026-33111—were published on May 7, 2026, and Microsoft reports that mitigations were deployed on the cloud side so that no customer action or patch installation is required. While that immediate remediation reduces near-term risk, the underlying issues expose a broader tension: AI-powered productivity tools often surface…

Saugata Datta4 min read242
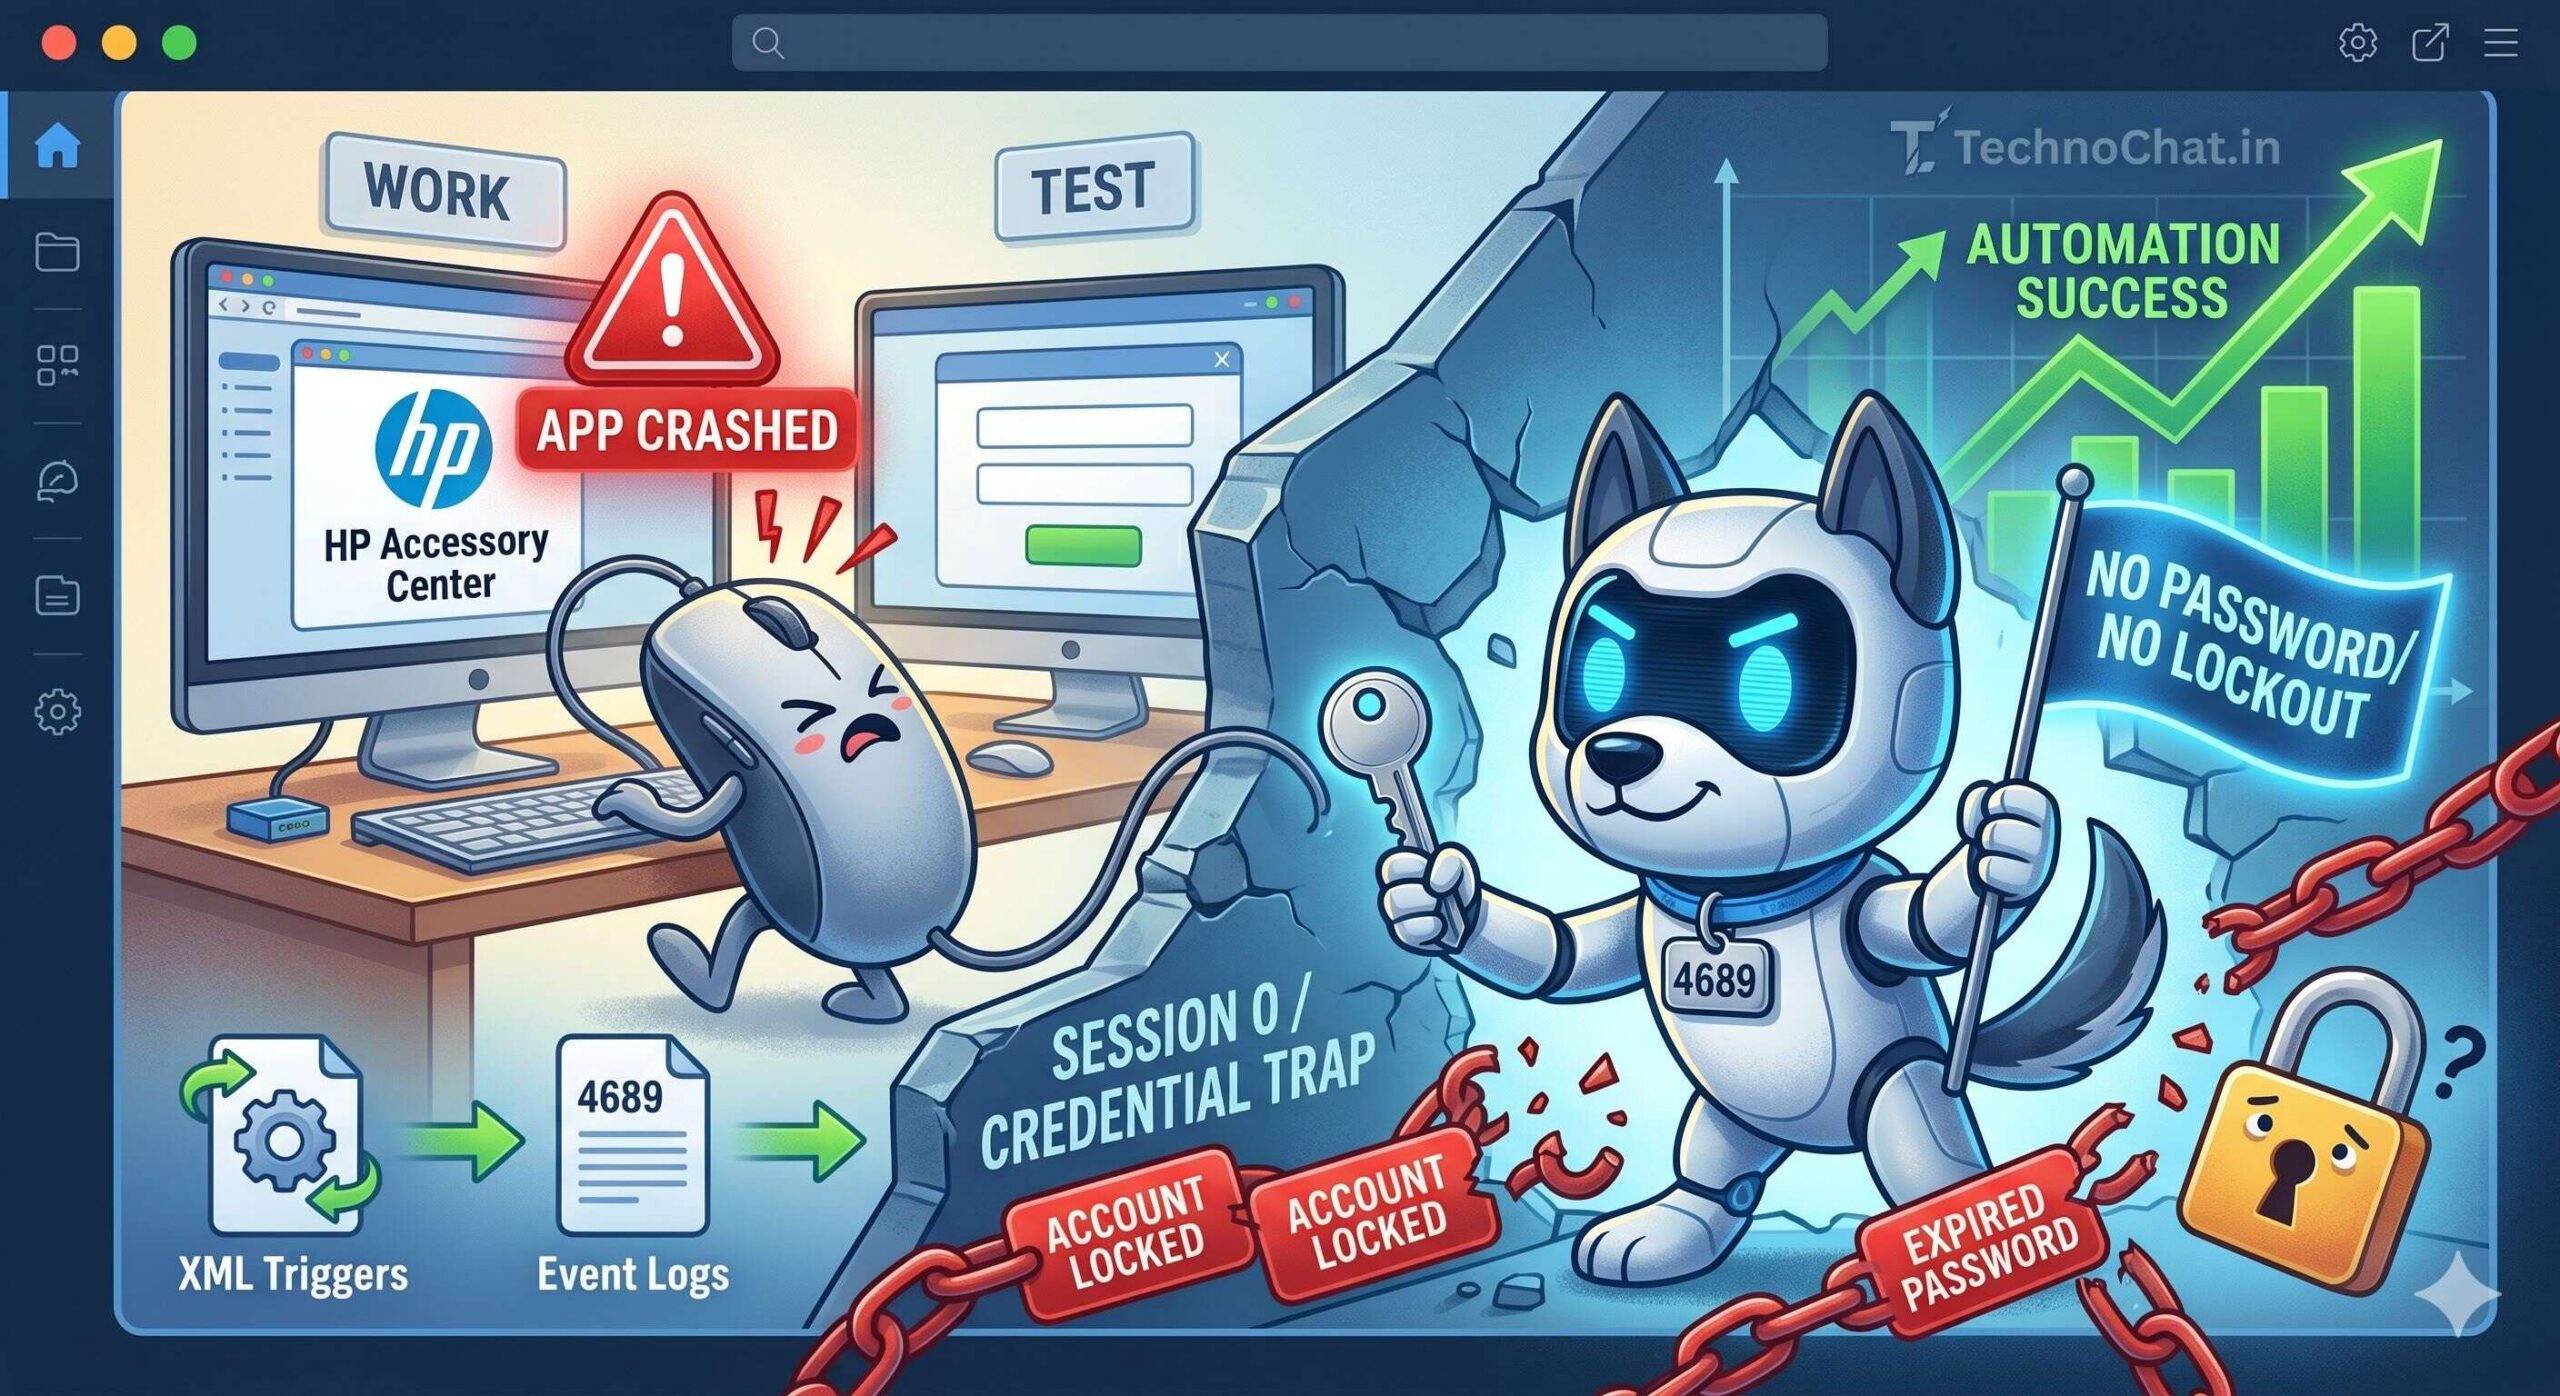
The Credential-Free Watchdog: Mastering Event-Driven App Automation

The Credential-Free Watchdog: Mastering Event-Driven App Automation

We have all been there. You are an automation lover. You have built a masterpiece — a Scheduled Task, perfectly configured, credentials entered, running like clockwork. You walk away like a hero. Then Monday morning hits. Your account is locked. Your coffee tastes like failure. I once left a mapped network drive in an SOE test build and completely forgot about it. Windows did not forget. Every night it faithfully…

Saugata Datta12 min read246
Accenture’s Big Bet: Rolling Copilot Out to 743,000 Employees and What It Means for Enterprise AI

Accenture’s Big Bet: Rolling Copilot Out to 743,000 Employees and What It Means for Enterprise AI

Accenture is expanding its use of Microsoft’s Copilot 365 AI assistant across its entire global workforce—about 743,000 people—a move that marks one of the largest enterprise deployments of the tool to date. The companies did not disclose financial terms, but the scale of the rollout sends a clear signal: major consultancies are moving from pilot projects to firmwide adoption, betting that AI can reshape day-to-day work and client services. Why…

Saugata Datta3 min read414
Microsoft’s New Group Policy to Remove Windows 11 Copilot from Managed Devices

Microsoft’s New Group Policy to Remove Windows 11 Copilot from Managed Devices

Microsoft has quietly given IT teams a precise tool to remove the consumer-facing Copilot app from managed Windows 11 machines. Rolled into the April 2026 Patch Tuesday updates and bundled with Windows 11 version 25H2 (KB5083769 and later), the RemoveMicrosoftCopilotApp policy lets administrators trigger a one-time uninstall of the Copilot app on devices that meet a small set of conditions. The change reflects a broader push to give enterprises control…

Saugata Datta3 min read303
Microsoft Outlook.com Hits Service Degradation: What Happened and How to Prepare

Microsoft Outlook.com Hits Service Degradation: What Happened and How to Prepare

On April 27, 2026, Microsoft acknowledged a service degradation affecting Outlook.com after users across multiple regions reported problems accessing their inboxes. The company’s Microsoft 365 Status account on X confirmed intermittent issues, and Microsoft’s service health dashboard classified the incident as a “Service Degradation” rather than a full outage. For many organizations and individual users, the disruption meant delayed email delivery, pages that failed to load, or an inability to…

Saugata Datta4 min read302
PhantomRPC: New Windows RPC Vulnerability Lets Attackers Escalate Privileges Across All Windows Versions

PhantomRPC: New Windows RPC Vulnerability Lets Attackers Escalate Privileges Across All Windows Versions

PhantomRPC is an architectural weakness in the Windows Remote Procedure Call (RPC) runtime that allows low-privileged processes to escalate to SYSTEM or Administrator by impersonating privileged clients. Disclosed by Kaspersky’s Haidar Kabibo at Black Hat Asia 2026, the flaw stems from how rpcrt4.dll handles connections to unavailable RPC servers: when a privileged process attempts an RPC call to a server that is offline or disabled, the RPC runtime can be…

Saugata Datta4 min read293
Hackers Leverage Microsoft Teams to Breach Organizations: Inside UNC6692’s SNOW Campaign

Hackers Leverage Microsoft Teams to Breach Organizations: Inside UNC6692’s SNOW Campaign

In late 2025 and into early 2026, a sophisticated intrusion campaign used the everyday familiarity of Microsoft Teams to turn routine collaboration into a direct route for enterprise compromise. By posing as IT helpdesk staff and exploiting users’ trust in external Teams invitations, the threat group tracked as UNC6692 moved from a simple chat message to full domain-level access—without exploiting a software vulnerability. The result was a carefully staged, cloud-hosted…

Saugata Datta5 min read377
🧰

Free Tools: IP, DNS, SSL

40+ free network and other tools in one place. No signup. Click explore or visit https://technochat.in/tools

Explore