GitLab has pushed an urgent set of security updates after disclosing a critical vulnerability in its AI Gateway that could allow authenticated users to run arbitrary commands on the gateway. Tracked as CVE-2026-90970 and rated CVSS 9.9, the flaw affects self-hosted AI Gateway deployments that support GitLab Duo AI features. While GitLab’s hosted gateways have already been patched, organizations running
Latest Articles
AWS
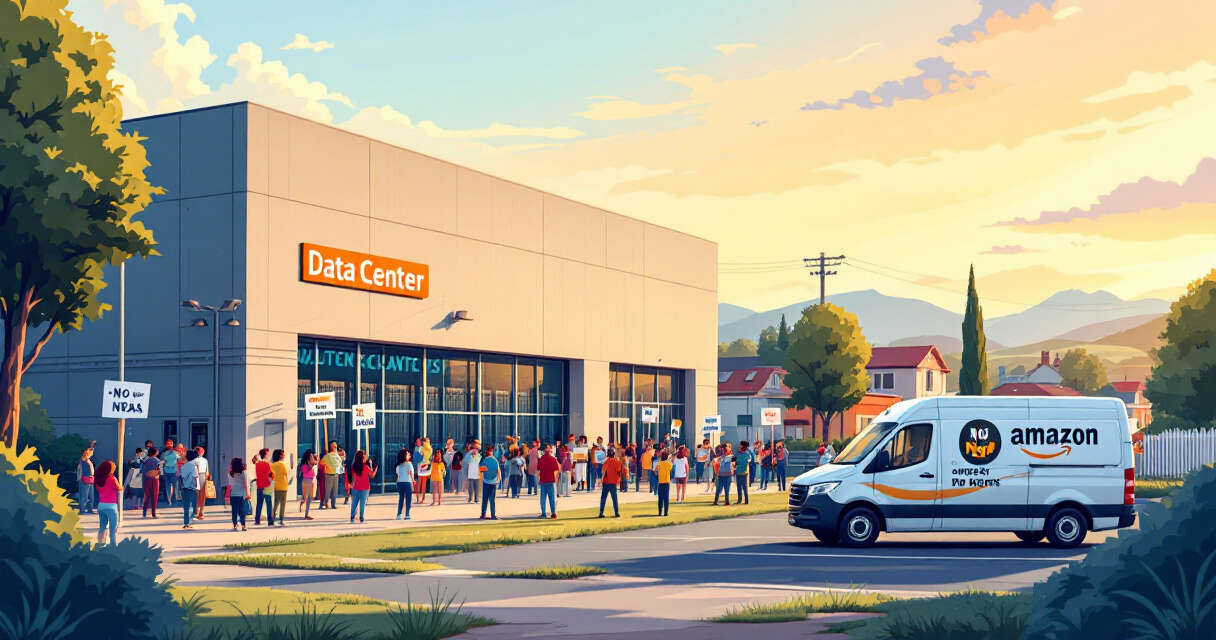
Amazon Drops NDAs as Data Center Backlash Grows
Amazon’s recent move to stop using nondisclosure agreements (NDAs) with government agencies marks a tactical shift in a widening dispute over the role of large data centers in local communities. Announced by AWS CEO Matt Garman in a blog post, the change comes as cities and states across the U.S. consider moratoriums and tougher scrutiny of new facilities. The announcement is short but strategic: Amazon is trying to blunt a narrative about secrecy and to position data centers as economic…
Continue readingCitrix NetScaler Reboots After Emergency 0-Day Patch: What Teams Need to Know
Citrix released emergency builds to address two actively exploited zero-day vulnerabilities in NetScaler appliances, but some organizations report that the patched appliances are repeatedly rebooting. What began as a rapid mitigation effort to stop remote command execution and DTLS-related attacks has morphed into an availability problem for some deployments—raising the difficult question defenders must balance: is this an operational outage
Debian Patches 1,313 Kernel Flaws: What Administrators Need to Know
Debian has just released a major kernel security update that aggregates fixes for 1,313 CVE entries, a headline figure that has drawn attention across the Linux community. The update — published as DSA-6528-1 and delivered for the Trixie stable release as Linux source package 6.12.111-1 — addresses a range of vulnerabilities that could, in different contexts, lead to privilege escalation,
Antino: A Stealthy Backdoor That Hides in Outlook and OneDrive
A new espionage campaign tracked by Cisco Talos has exposed a sophisticated Windows backdoor, nicknamed Antino, that uses Microsoft 365 services as its covert communications channel. Targeting government and policy organizations across Asia — including Taiwan, India, the Philippines, Cambodia, Pakistan, Thailand, and Myanmar — the activity centers on highly tailored spear‑phishing lures and a multi-stage infection chain that culminates
Apple tightens Full Disk Access controls to block potential AI agent abuse
When an AI assistant began referencing private iMessage threads without a clear explanation of how it accessed them, it set off a rapid chain of scrutiny and vendor responses. Apple has moved to tighten macOS’s Full Disk Access (FDA) permissions after concerns that some third-party apps could misuse that powerful system-level privilege to read private files, messages, and browsing histories.
Attackers Exploit SharePoint Authentication Bypass After Public PoC Release
Microsoft’s SharePoint platform is facing active exploitation following the public release of a proof-of-concept (PoC) for a critical authentication bypass vulnerability tracked as CVE-2026-55040. Patched in July’s Patch Tuesday, the flaw allows unauthenticated actors to impersonate SharePoint users by forging JSON Web Tokens (JWTs). Since the PoC surfaced, security researchers and telemetry providers have observed real-world attempts that underscore the