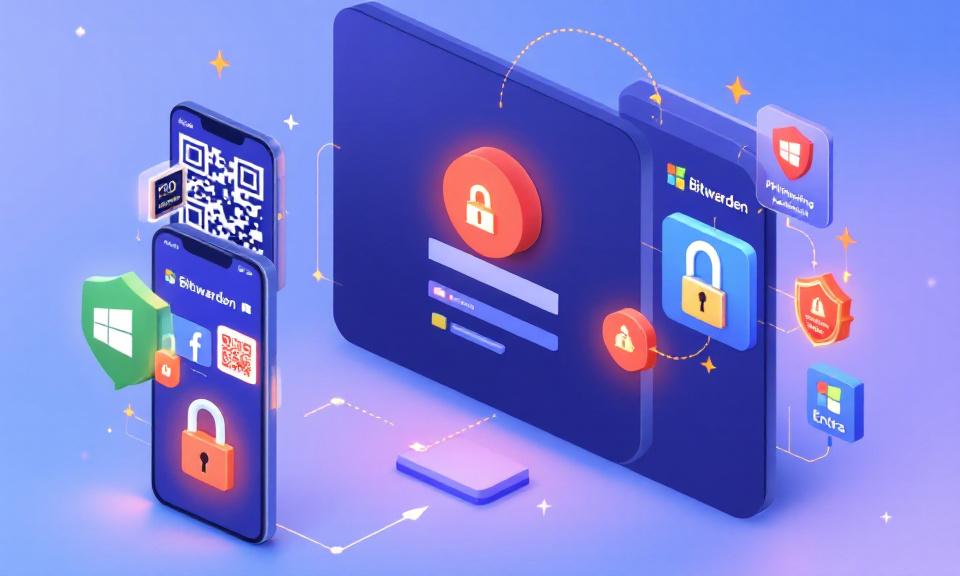
Bitwarden now supports using passkeys stored in its vault to sign into Windows 11 devices, enabling passwordless, phishing-resistant authentication. The feature is available to all Bitwarden plans, including the free tier.
How it works
- On the Windows sign-in screen, users choose the security key sign-in option and scan a QR code with a mobile device.
- The passkey stored in the user’s Bitwarden encrypted vault responds to the cryptographic authentication challenge instead of a password.
- Bitwarden acts as the passkey provider in the Windows authentication flow, keeping the credential in the synced vault rather than binding it to a single device, which enables recovery from other devices if a phone is lost.
Requirements
- Devices must be joined to Microsoft Entra ID.
- FIDO2 security key sign-in must be enabled in the environment.
- A registered Entra ID passkey must be stored in the user’s Bitwarden vault.
Why it matters
Replacing password entry with cryptographic passkeys removes shared secrets from the sign-in process and significantly reduces the risk of credential exposure to phishing. Because credentials are stored in the synced vault, users can recover access from alternate devices if needed.
Availability and notes
Microsoft is rolling out passkey login for Windows this month; adoption depends on Entra ID configuration. The capability builds on the Windows passkey provider API introduced in late 2025, extending third‑party passkey management to the OS sign-in layer.
 Licensed under CC BY-ND 4.0 International
Antino: A Stealthy Backdoor That Hides in Outlook and OneDrive
A new espionage campaign tracked by Cisco Talos has exposed a sophisticated…
Attackers Exploit SharePoint Authentication Bypass After Public PoC Release
Microsoft’s SharePoint platform is facing active exploitation following the public release of…
Breaking the code: how a multi-stage “code of conduct” phishing campaign led to AiTM token compromise
Phishing has evolved from crude scams to carefully engineered deceptions that mimic…
Critical Microsoft 365 Copilot Flaws: What Organizations Need to Know
Microsoft has disclosed and silently remediated three critical information-disclosure vulnerabilities in Microsoft…
PhantomRPC: New Windows RPC Vulnerability Lets Attackers Escalate Privileges Across All Windows Versions
PhantomRPC is an architectural weakness in the Windows Remote Procedure Call (RPC)…
Hackers Leverage Microsoft Teams to Breach Organizations: Inside UNC6692’s SNOW Campaign
In late 2025 and into early 2026, a sophisticated intrusion campaign used…
Microsoft Confirms July Windows Update Is Causing Some Dell Laptops to Shut Down and Overheat
Microsoft has acknowledged that a recent Windows 11 preview update has caused…
Atlassian Urges Immediate Patching After Critical Arbitrary File-Access Flaw
Atlassian has released emergency fixes for a critical arbitrary file access vulnerability…