A new espionage campaign tracked by Cisco Talos has exposed a sophisticated Windows backdoor, nicknamed Antino, that uses Microsoft 365 services as its covert communications channel. Targeting government and policy organizations across Asia — including Taiwan, India, the Philippines, Cambodia, Pakistan, Thailand, and Myanmar — the activity centers on highly tailored spear‑phishing lures and a multi-stage infection chain that culminates
Category: Hacking and Exploits
Web-Hacking, 0-Day, Malware, Ransomware, Exploit, Vulnerabilities, Privilege-Flaw, Privilege-Escalation, Zero-Day, Exploit, Jailbreak, Penetration-Testing, Trojan, Spyware, Rootkit, Worm, Backdoor, Payload, Obfuscation, DDoS, Phishing, MITM, Spoofing, Brute-force, Port-Scan, SQLi, XSS, CSRF, Path-Traversal, LFI, RFI, Insecure-Deserialization, Buffer-Overflow, CVE, Exploit-Kit, Shellcode, bug bounty, ethical hacking, CTF, capture the flag, offensive security, red team exercise, exploit development, reverse engineering, vulnerability research, credential harvesting
Attackers Exploit SharePoint Authentication Bypass After Public PoC Release
Microsoft’s SharePoint platform is facing active exploitation following the public release of a proof-of-concept (PoC) for a critical authentication bypass vulnerability tracked as CVE-2026-55040. Patched in July’s Patch Tuesday, the flaw allows unauthenticated actors to impersonate SharePoint users by forging JSON Web Tokens (JWTs). Since the PoC surfaced, security researchers and telemetry providers have observed real-world attempts that underscore the
Akira Ransomware Uses Windows Safe Mode to Shut Down EDR Before Launching Encryptor
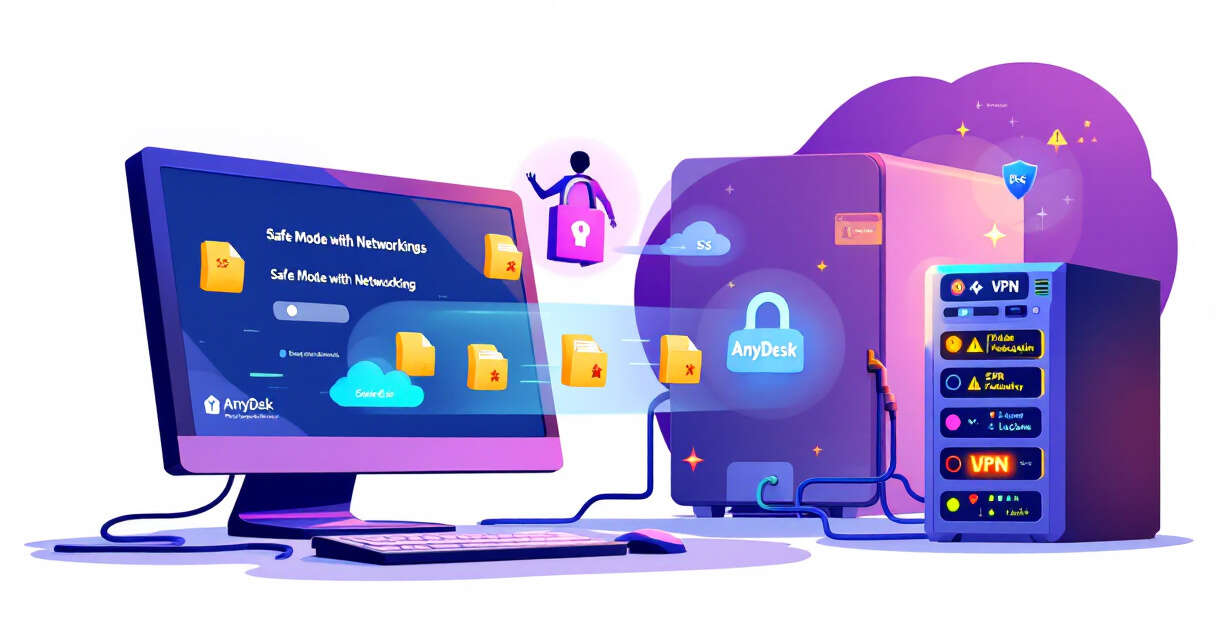
Akira’s latest tactics expand the ransomware playbook: instead of relying solely on kernel drivers or signed binaries to disable protections, an affiliate in a recent intrusion rebooted a compromised host into Safe Mode with Networking to silence endpoint defenses while keeping network access for remote control and exfiltration. The operation began with a successful credential-spraying attack against an exposed SonicWall
WordPress Imagick RCE (CVE-2026-65640): What Site Owners Need to Know
WordPress has just released a security-focused update — version 7.0.4 — to close a remote code execution flaw that can be triggered when images are processed with the Imagick extension and Ghostscript. The vulnerability, tracked as CVE-2026-65640 and described in GHSA-8vr3-7mxf-gx8w, was responsibly disclosed by researchers at pwn.ai. While exploitation requires an authenticated Author-level account or higher, the bug’s mechanics
Cisco Issues Emergency Fix for Firewall Zero-Day Under Active Attack
Cisco has issued an urgent warning to organizations worldwide following the discovery of a zero-day vulnerability in its core firewall software. Tracked as CVE-2026-20349, the flaw is currently being exploited in the wild, allowing unauthenticated attackers to trigger a denial-of-service (DoS) condition. Because this vulnerability affects the perimeter of the network—the very place designed to keep threats out—security teams are
Critical Adobe Commerce Flaws Put Online Stores at Risk — Patch Now
Adobe has rolled out an urgent August 2026 security update for Adobe Commerce and Magento Open Source to fix a cluster of authorization and stored cross-site scripting (XSS) flaws that, together, present a significant threat to e-commerce environments. The most severe issue, CVE-2026-71362, is an incorrect-authorization vulnerability rated 9.1 (CVSS) that could allow an unauthenticated attacker to escalate privileges and