ClickFix attacks have evolved from simple social-engineering lures into highly creative delivery mechanisms that turn a user’s own system into the execution environment. Recent Microsoft telemetry describes a variant that stages malicious scripts inside a victim’s browser cache—disguised as innocuous PNG files—and then convinces the user to paste a short command that triggers execution of that cached payload. By hiding
Category: DevOps and Infrastructure
DevOps, Terraform, CI/CD, GitHub Actions, GitLab CI, Jenkins, ArgoCD, FluxCD, Docker, Docker Compose, Podman, Vagrant, Packer, Nexus, SonarQube, HashiCorp Vault, Consul, Prometheus, Grafana, Loki, Alertmanager, ELK Stack, Datadog, New Relic, OpenTelemetry, SRE, site reliability engineering, infrastructure as code, IaC, GitOps, platform engineering, observability, monitoring
Critical GitLab AI Gateway Flaw: What Administrators Need to Do Now
GitLab has pushed an urgent set of security updates after disclosing a critical vulnerability in its AI Gateway that could allow authenticated users to run arbitrary commands on the gateway. Tracked as CVE-2026-90970 and rated CVSS 9.9, the flaw affects self-hosted AI Gateway deployments that support GitLab Duo AI features. While GitLab’s hosted gateways have already been patched, organizations running
The Credential-Free Watchdog: Mastering Event-Driven App Automation
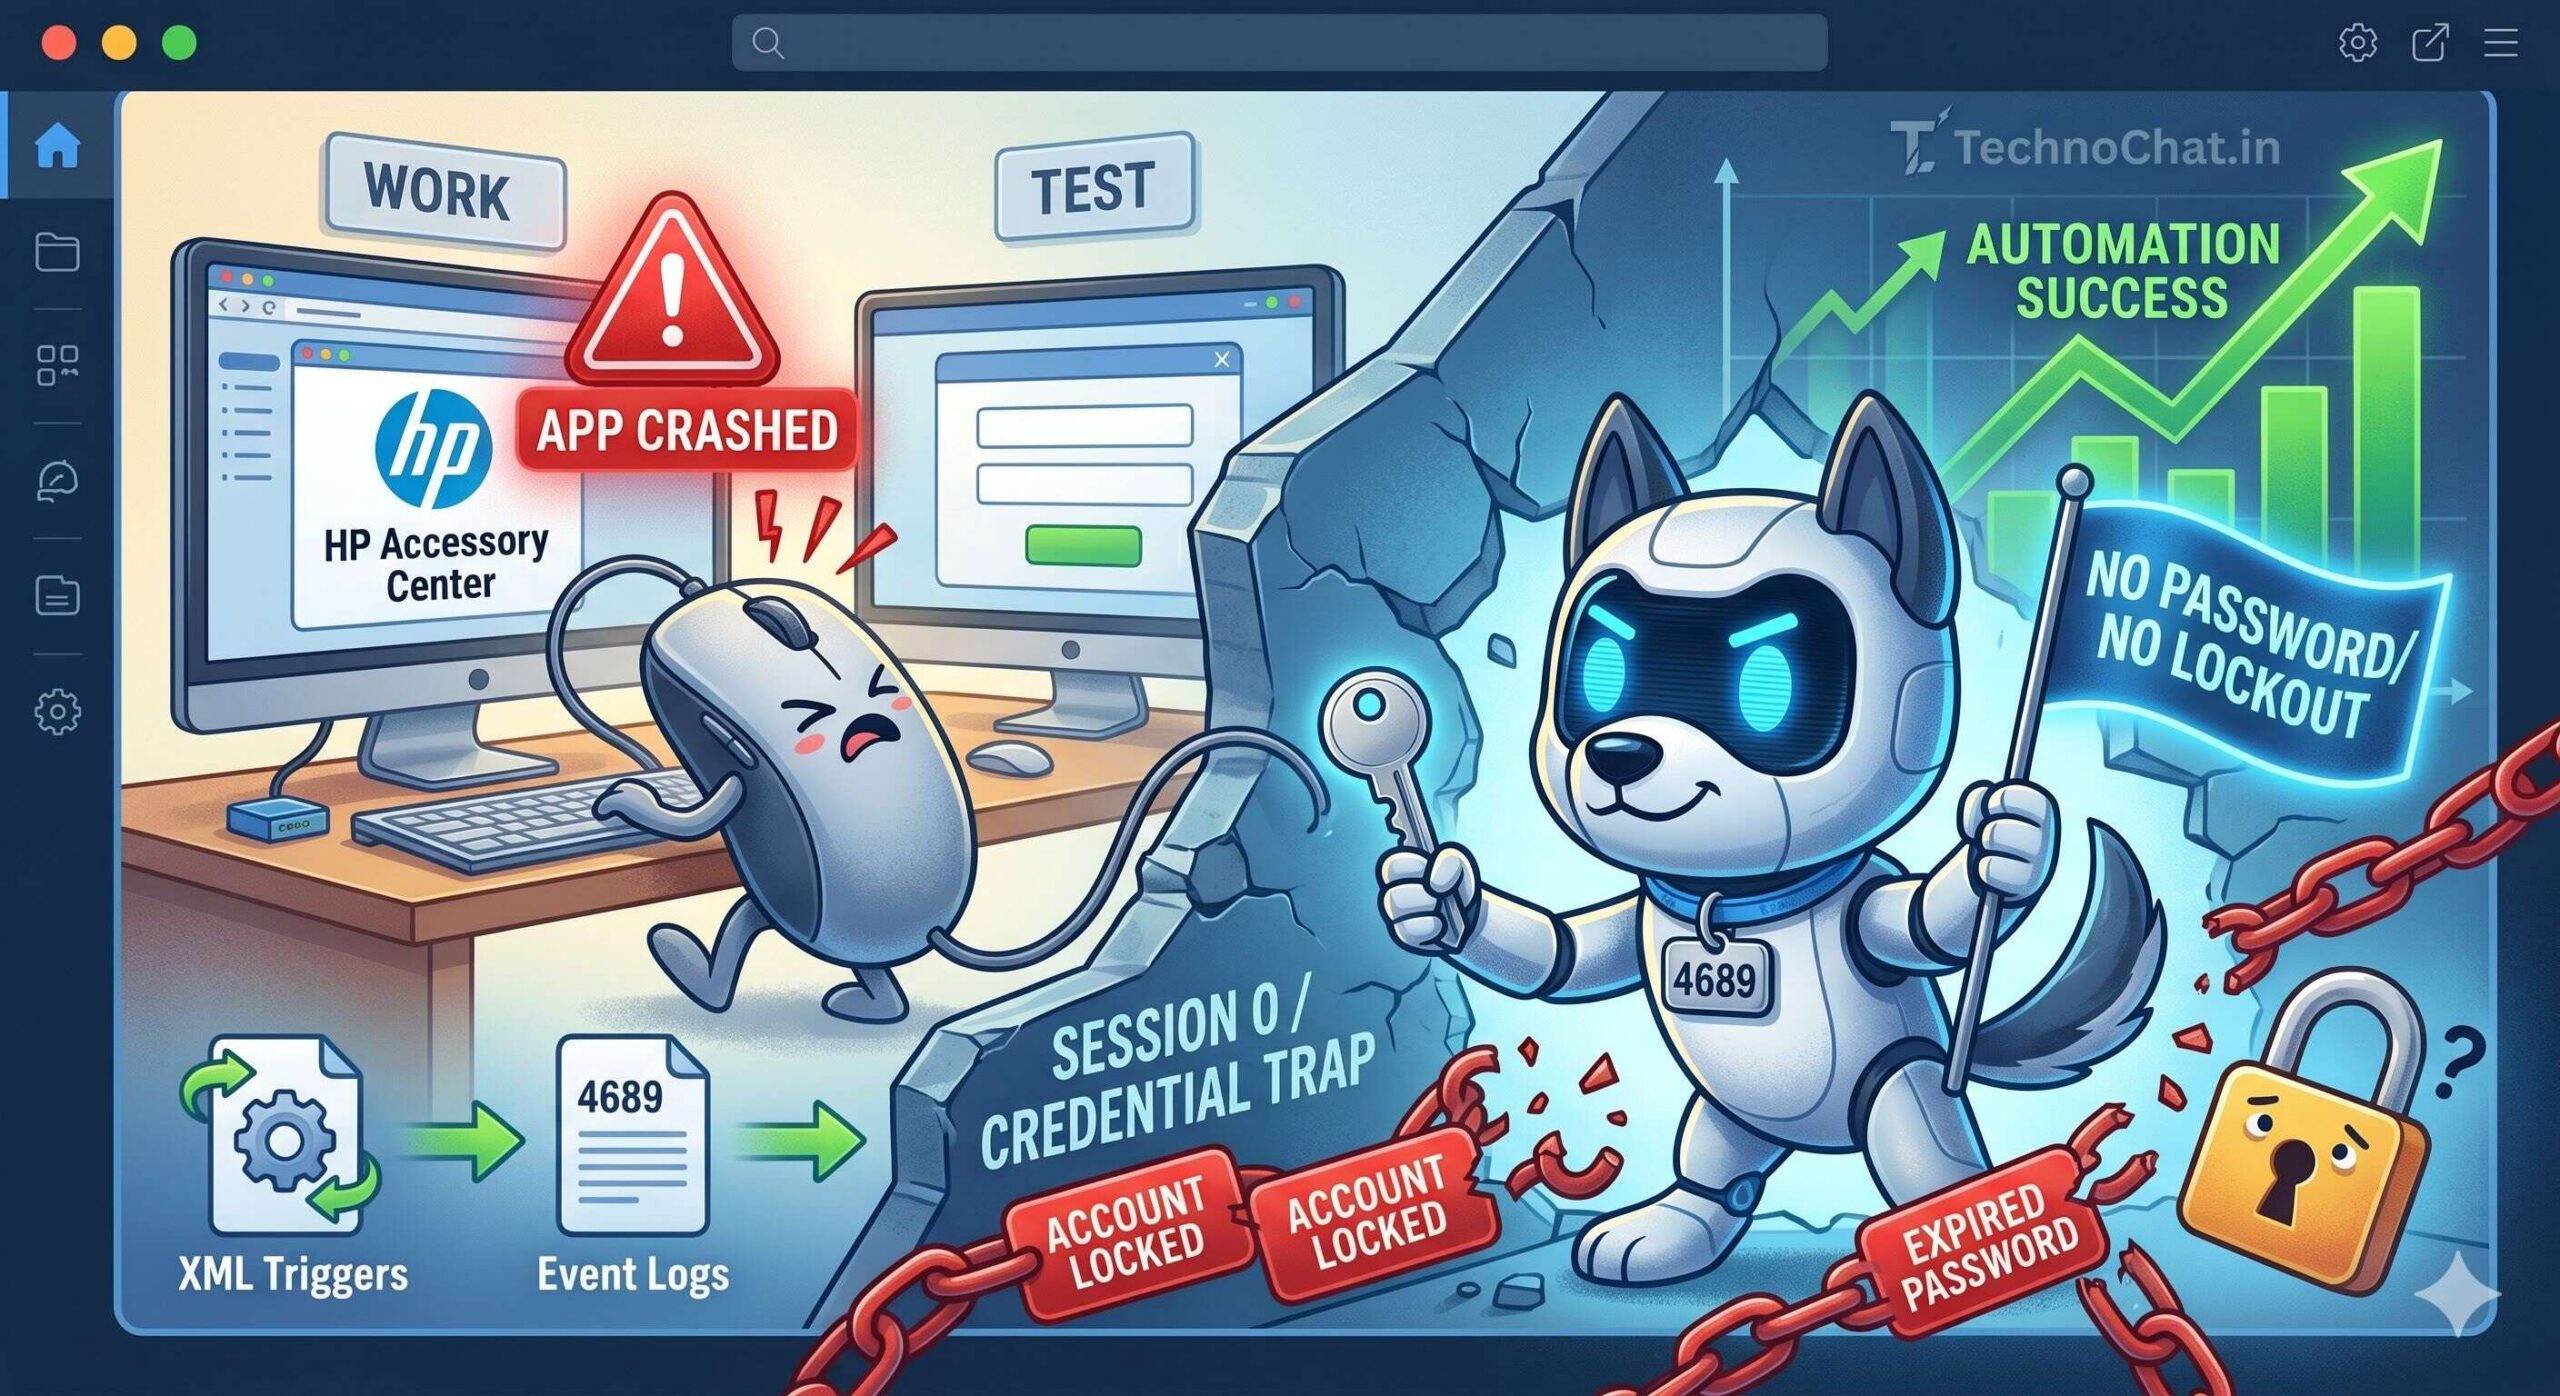
We have all been there. You are an automation lover. You have built a masterpiece — a Scheduled Task, perfectly configured, credentials entered, running like clockwork. You walk away like a hero. Then Monday morning hits. Your account is locked. Your coffee tastes like failure. I once left a mapped network drive in an SOE test build and completely forgot
How the Google Gemini CLI Flaw Turned CI/CD Pipelines into Remote Code Execution Risk
A critical remote code execution (RCE) vulnerability in the Google Gemini CLI and its associated GitHub Action exposed a startling weakness in how AI tooling can interact with developer infrastructure. Rated with the maximum CVSS score of 10.0, the bug allowed unprivileged external actors to execute commands on the machines running CI/CD workflows. This wasn’t a prompt-injection trick against a
Bitwarden CLI Compromised in Supply Chain Attack via GitHub Actions
Socket and other researchers have confirmed that the Bitwarden CLI package published to npm — @bitwarden/cli version 2026.4.0 — was compromised in a supply chain attack that abused a GitHub Action in Bitwarden’s CI/CD pipeline. The malicious release injected a file named bw1.js into the package, exposing tokens, cloud credentials, SSH keys and other sensitive artifacts. While Bitwarden’s Chrome extension,
109 Fake GitHub Repositories Used to Deliver SmartLoader and StealC Malware
A large-scale campaign recently uncovered shows how attackers abused the trust developers place in open-source hosting to distribute two dangerous malware families, SmartLoader and StealC. By cloning legitimate projects and burying malicious ZIP archives deep inside repository structures, the threat actor made harmful downloads look like routine releases. For many victims the repository looked authentic at a glance: real source