Author

Saugata Datta

I’m an IT/DevOps professional with many years of hands-on experience across Windows, Linux, Automation, Backup and Cloud. I love building real-world automations to make infrastructure reliable, secure, and self-healing. Through this blog, I share practical learnings from enterprise projects and my home-lab experiments on Cloudflare, Self-Hosting and everything in between. Always tinkering, always improving.
Page 10
Google patches an Android flaw that can run code without user action

Google patches an Android flaw that can run code without user action

A critical Android flaw could let an attacker run code on a phone remotely without any user action, according to Google’s November security bulletin. The flaw is CVE-2026-58868, and Google says it affects Android 14 through 17. Security patch level 2026-11-01 or later includes the fix for CVE-2026-58868. Phone makers and carriers deliver that update on their own schedules, and Google says older versions such as Android 12 and 13…
Saugata Datta4 min read124
Russian police arrest VasyGrek suspects and seize criminal equipment

Russian police arrest VasyGrek suspects and seize criminal equipment

Russian authorities have arrested three suspected members of the threat group known as VasyGrek and dismantled its criminal infrastructure. The group is also known as Fluffy Wolf and has targeted Russian and international companies since 2016. The Ministry of Internal Affairs of the Russian Federation, or MVD, says the suspects are believed to have stolen money from organizational accounts and created, distributed, and used malicious software. In one September 2025…

Saugata Datta3 min read118
LLMJacking technique triggers million dollar corporate cloud expenses

LLMJacking technique triggers million dollar corporate cloud expenses

Unauthorized access to corporate large language models, a technique called LLMJacking, is being used to resell AI services and generate massive cloud bills for victims. Google Threat Intelligence Group (GTIG) reported on November 2 that these attacks have affected various industries across North America, South America, and Asia Pacific, leading to costs reaching $1 million. Financial impact on victim organizations Mandiant investigated multiple 2026 incidents where stolen credentials resulted in…

Saugata Datta3 min read124
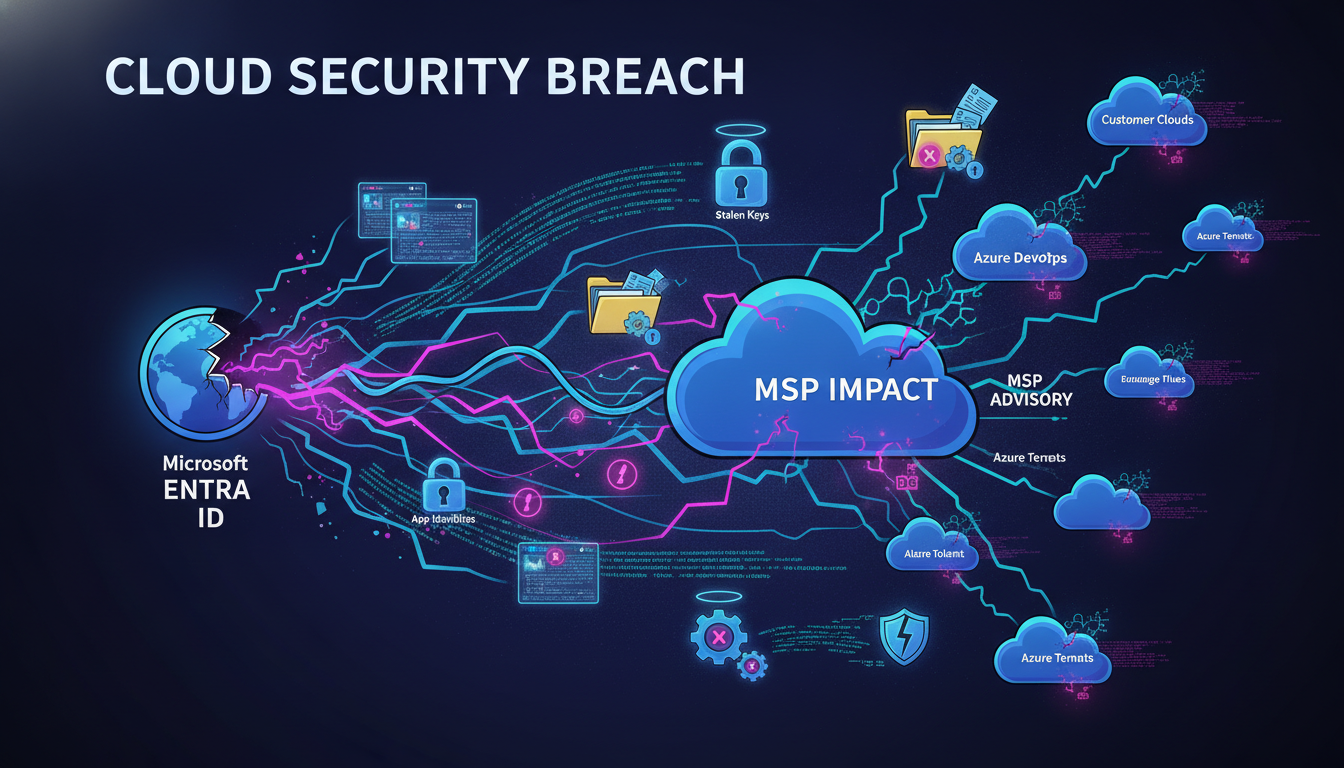
Stolen Entra ID credentials widened access to 27 organizations

Stolen Entra ID credentials widened access to 27 organizations

Todyl’s latest investigation update describes an ongoing campaign that has used stolen Microsoft Entra ID application credentials and Azure DevOps identities to reach Microsoft 365 and Azure environments. The activity has affected at least 27 organizations, and it has targeted managed service providers, or MSPs, and their customers since November 1, 2026. Attack paths across cloud tenants The operator targeted about 45 app registrations across roughly 18 organizations, and more…

Saugata Datta3 min read133
Philippine government breach exposed migrant worker data and backup records

Philippine government breach exposed migrant worker data and backup records

An unknown threat actor appears to have taken nearly 69GB of sensitive data from the Philippine Overseas Employment Administration, including worker information, contracts, and financial records. Hunt.io said the material was copied from backup databases through a Singaporean staging server used in the breach, and the trail ended there. Data moved through a staging server Hunt.io’s Oct. 28 analysis said the attacker copied 27 backup databases in 24 minutes. The…

Saugata Datta3 min read132
French blood plasma freezers changed settings after supplier compromise

French blood plasma freezers changed settings after supplier compromise

Hackers reportedly changed temperature settings on refrigeration equipment used by the French Blood Establishment, EFS, from around −30°C to 110°C after targeting its cooling service provider, Coolworld. The incident happened overnight between November 1 and 2, 2026, and it raised concerns about frozen plasma stored for patient transfusions. Staff in Bourgogne-Franche-Comté were among those who noticed the problem. France’s Health Ministry said they detected the abnormal temperatures in time and…

Saugata Datta3 min read127
Binance says fake recruiter tricked employee into wallet breach

Binance says fake recruiter tricked employee into wallet breach

Binance says North Korean hackers used a fake job interview to lure a software engineer into installing malware that led to the compromise of its wallet infrastructure and the theft of about $6.34 billion in digital assets. The exchange said the intrusion started in September and that the attack on October 29 used social engineering, malicious software, and compromised internal systems. The company tied the case to an incident report…

Saugata Datta3 min read129
CERT-In turns to Claude Mythos for controlled cybersecurity testing

CERT-In turns to Claude Mythos for controlled cybersecurity testing

India's cybersecurity agency, the Indian Computer Emergency Response Team, also known as CERT-In, has reportedly secured access to Claude Mythos. The Anthropic model is being used to detect vulnerabilities and weaknesses across systems, and the testing is taking place in a controlled environment. Anthropic’s cybersecurity model and CERT-In’s access Claude Mythos is Anthropic’s frontier AI model for cybersecurity, and it was released in April this year. CERT-In had demanded fair…

Saugata Datta2 min read137
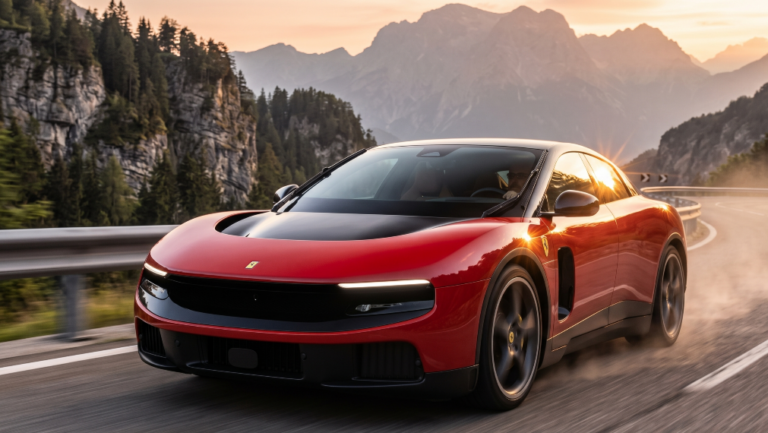
Ferrari’s Luce EV reaches full allocation for 2027

Ferrari’s Luce EV reaches full allocation for 2027

Ferrari’s Luce EV, the company’s first electric car, is fully allocated for 2027. CEO Benedetto Vigna said every Luce Ferrari plans to build next year already has a buyer, even though the model drew mockery and broad criticism when it debuted in May. Luce demand and delivery timing The five-seater EV was designed by Jony Ive, Apple’s longtime design chief. It starts at about $615,000, and the first deliveries are…

Saugata Datta2 min read127
cPGuard update compromise spreads backdoor and data theft

cPGuard update compromise spreads backdoor and data theft

OpsShield says attackers compromised the cPGuard web security suite’s update distribution infrastructure and used it to push a malicious script and a backdoor. The company said the attack began on November 2 at 02:06 UTC, affected versions 5.88.12 through 5.88.19, and may have missed some servers because update checks run at specific intervals. cPGuard update compromise OpsShield said it detected the compromise and stopped the malicious distribution within 12 hours…

Saugata Datta2 min read130
Anthropic builds a system to verify which AI model made an output

Anthropic builds a system to verify which AI model made an output

Anthropic is developing an open source system called FlashProve to verify which AI model produced a given output. The project is meant to give users a cryptographic proof that an answer came from the specific model they think they were using, according to a blog post published Tuesday. How FlashProve is meant to work The researchers describe FlashProve as a form of provable inference. That means the system is intended…

Saugata Datta2 min read133
Reddit begins testing search ads as traffic and growth pressure rise

Reddit begins testing search ads as traffic and growth pressure rise

Reddit is testing ad placements inside its search results pages after warning investors about declining search traffic and a weaker-than-expected revenue forecast. The company said the new placements are meant to help it earn more from existing users as Google’s AI search changes how people find Reddit content. Reddit’s search ad test On Tuesday, Reddit said advertisers can now reach people as they search on the platform for products, recommendations,…

Saugata Datta2 min read143
🧰

Free Tools: IP, DNS, SSL

40+ free network and other tools in one place. No signup. Click explore or visit https://technochat.in/tools

Explore