Category

Cloudflare

Cloudflare, Cloudflare Workers, Cloudflare Pages, Cloudflare Tunnel, Cloudflare WAF, Cloudflare CDN, Cloudflare DNS, Cloudflare Zero Trust, Cloudflare Access, Cloudflare Gateway, Cloudflare R2, Cloudflare KV, Cloudflare D1, Cloudflare Stream, Cloudflare Images, Cloudflare Cache, Cloudflare Rules, Cloudflare Firewall Rules, Cloudflare Transform Rules, Cloudflare Rate Limiting, Cloudflare DDoS, Cloudflare SSL, Cloudflare WARP, Cloudflare Analytics, Cloudflare AI Gateway, Workers AI, Wrangler, Cloudflare Dashboard

17 stories
Barracuda Email Security Gateway flaws prompt root-access warnings

Barracuda Email Security Gateway flaws prompt root-access warnings

Barracuda has confirmed that security flaws in its Email Security Gateway, also known as ESG, are being actively exploited. The company said on November 9, 2026, in an update issued at 9:00 p.m. EST that the activity affected a small number of organizations, and that attackers could combine two vulnerabilities to gain root access without logging in. Exposure at the management interface The two tracked issues are CVE-2026-116606 and CVE-2026-111560.…
Saugata Datta3 min read56
Cloudflare’s Zero Wire tracks critical CVEs and security fixes

Cloudflare’s Zero Wire tracks critical CVEs and security fixes

Cloudflare has launched Zero Wire, a public vulnerability intelligence feed designed to help security teams track critical CVEs, understand exploitation activity, and find security fixes. Announced on November 3, 2026, it sits within Cloudflare Radar’s security section and brings technical evidence, vendor guidance, and recommended actions into readable briefings. The service is built around a familiar problem. When a serious vulnerability appears, defenders have to assemble scattered advisories while checking…

Saugata Datta3 min read114
Barracuda devices face root-access flaws after patch warning

Barracuda devices face root-access flaws after patch warning

Barracuda Networks warned customers to patch two vulnerabilities that can let attackers run commands with root privileges on affected devices. The company said one flaw is a critical Email Security Gateway authentication weakness, and the other allows threat actors with admin permissions to inject operating system commands that run as root. Exposure depends on access to the administrative interfaces of the targeted devices. Barracuda said successful exploitation also requires that…

Saugata Datta2 min read132
Cloudflare’s Q3 Surge: 18.2 Million Network-Layer DDoS Attacks and Changing Threat Patterns

Cloudflare’s Q3 Surge: 18.2 Million Network-Layer DDoS Attacks and Changing Threat Patterns

Threat actors ramped up automated disruption in the third quarter of 2026, with Cloudflare reporting a dramatic rise in the frequency and variety of distributed denial-of-service (DDoS) attacks. The company mitigated 18.2 million network-layer (L3) DDoS attacks and handled 14.4 trillion HTTP DDoS requests during the quarter — a scale that underscores how persistent and rapidly evolving DDoS activity has become. Quarterly volume and pace Cloudflare’s numbers translate to roughly…

Saugata Datta2 min read202
AWS Powers Amazon’s Record Margins While AI Spending Drains Cash Flow

AWS Powers Amazon’s Record Margins While AI Spending Drains Cash Flow

Amazon’s third-quarter 2026 results painted a study in contrasts: robust top-line growth and record operating margins driven largely by AWS, paired with mounting cash-flow pressure as heavy AI investments and capital expenditures weigh on liquidity. Revenue rose to $201.9 billion, operating income jumped sharply, yet free cash flow turned negative for the trailing year—signs that Amazon is balancing a profitable core with aggressive, expensive bets on AI infrastructure. A quarter…

Saugata Datta3 min read217
AI-Assisted PHP2Shell and Fragnesia Chain Roots 25 Servers, Penetrates U.S. Government-Affiliated Network

AI-Assisted PHP2Shell and Fragnesia Chain Roots 25 Servers, Penetrates U.S. Government-Affiliated Network

Cybersecurity researchers have detailed an AI-assisted campaign that combined PHP2Shell exploitation with a Linux kernel privilege escalation to gain root on 25 servers and pivot into an internal network tied to a U.S. government-affiliated environment. The activity was observed in late October 2026 and, according to the Israeli firm Dream, demonstrates a tailored, multi-stage intrusion that fused custom exploit development with automated reconnaissance at scale. Attack overview Dream attributes the…

Saugata Datta4 min read238
Cloudflare Issues Emergency WAF Rules for CVE-2026-111497 Brotli Flaw

Cloudflare Issues Emergency WAF Rules for CVE-2026-111497 Brotli Flaw

Cloudflare has released an emergency Web Application Firewall (WAF) ruleset update tied to CVE-2026-111497, a memory flaw in Node.js’s Brotli decoder. Published on October 25, 2026, the update adds two new detections designed to surface potentially risky traffic related to the vulnerability while leaving blocking decisions to customers by default. What Cloudflare added The release introduces two rules: one that detects requests declaring a Brotli-compressed request body and another that…

Saugata Datta3 min read232
Kentik Links Foreign Traffic Floods to North Korea .kp Outage

Kentik Links Foreign Traffic Floods to North Korea .kp Outage

Multiple waves of traffic this week knocked large parts of North Korea’s public internet offline, leaving more than 40 .kp websites intermittently unreachable for roughly 32 hours. The outages began in the early hours of October 20 (02:01 UTC) and affected core services including the Ministry of Foreign Affairs and the Korean Central News Agency. Internet measurement firm Kentik, through its internet analysis director Doug Madory, traced sudden traffic floods…

Saugata Datta3 min read286
Critical GitLab AI Gateway Flaw: What Administrators Need to Do Now

Critical GitLab AI Gateway Flaw: What Administrators Need to Do Now

GitLab has pushed an urgent set of security updates after disclosing a critical vulnerability in its AI Gateway that could allow authenticated users to run arbitrary commands on the gateway. Tracked as CVE-2026-90970 and rated CVSS 9.9, the flaw affects self-hosted AI Gateway deployments that support GitLab Duo AI features. While GitLab’s hosted gateways have already been patched, organizations running their own gateways must act immediately to mitigate a high-impact…

Saugata Datta4 min read432
Cloudflare makes post‑quantum IPsec generally available

Cloudflare makes post‑quantum IPsec generally available

For years, the internet’s move to post‑quantum cryptography focused first on TLS, but site‑to‑site networking has lagged behind. Today Cloudflare is announcing general availability of post‑quantum encryption for Cloudflare IPsec, bringing hybrid ML‑KEM protection to WAN tunnels so organizations can defend against “harvest‑now, decrypt‑later” attacks without buying specialized hardware. This update moves another critical piece of enterprise networking closer to a quantum‑resistant future as Cloudflare continues its push toward full…

Saugata Datta4 min read555
Agents, Stripe Projects, and zero-friction Cloudflare provisioning

Agents, Stripe Projects, and zero-friction Cloudflare provisioning

Agents can now take a project from idea to live production on Cloudflare without a human manually opening a dashboard, entering card details, or copying API keys. In partnership with Stripe’s new Projects flow, Cloudflare built a protocol that lets an orchestrator platform (like Stripe Projects) attest to a signed‑in user’s identity, provide a payment token, and expose a catalog of available services. An agent using that catalog can provision…

Saugata Datta5 min read582
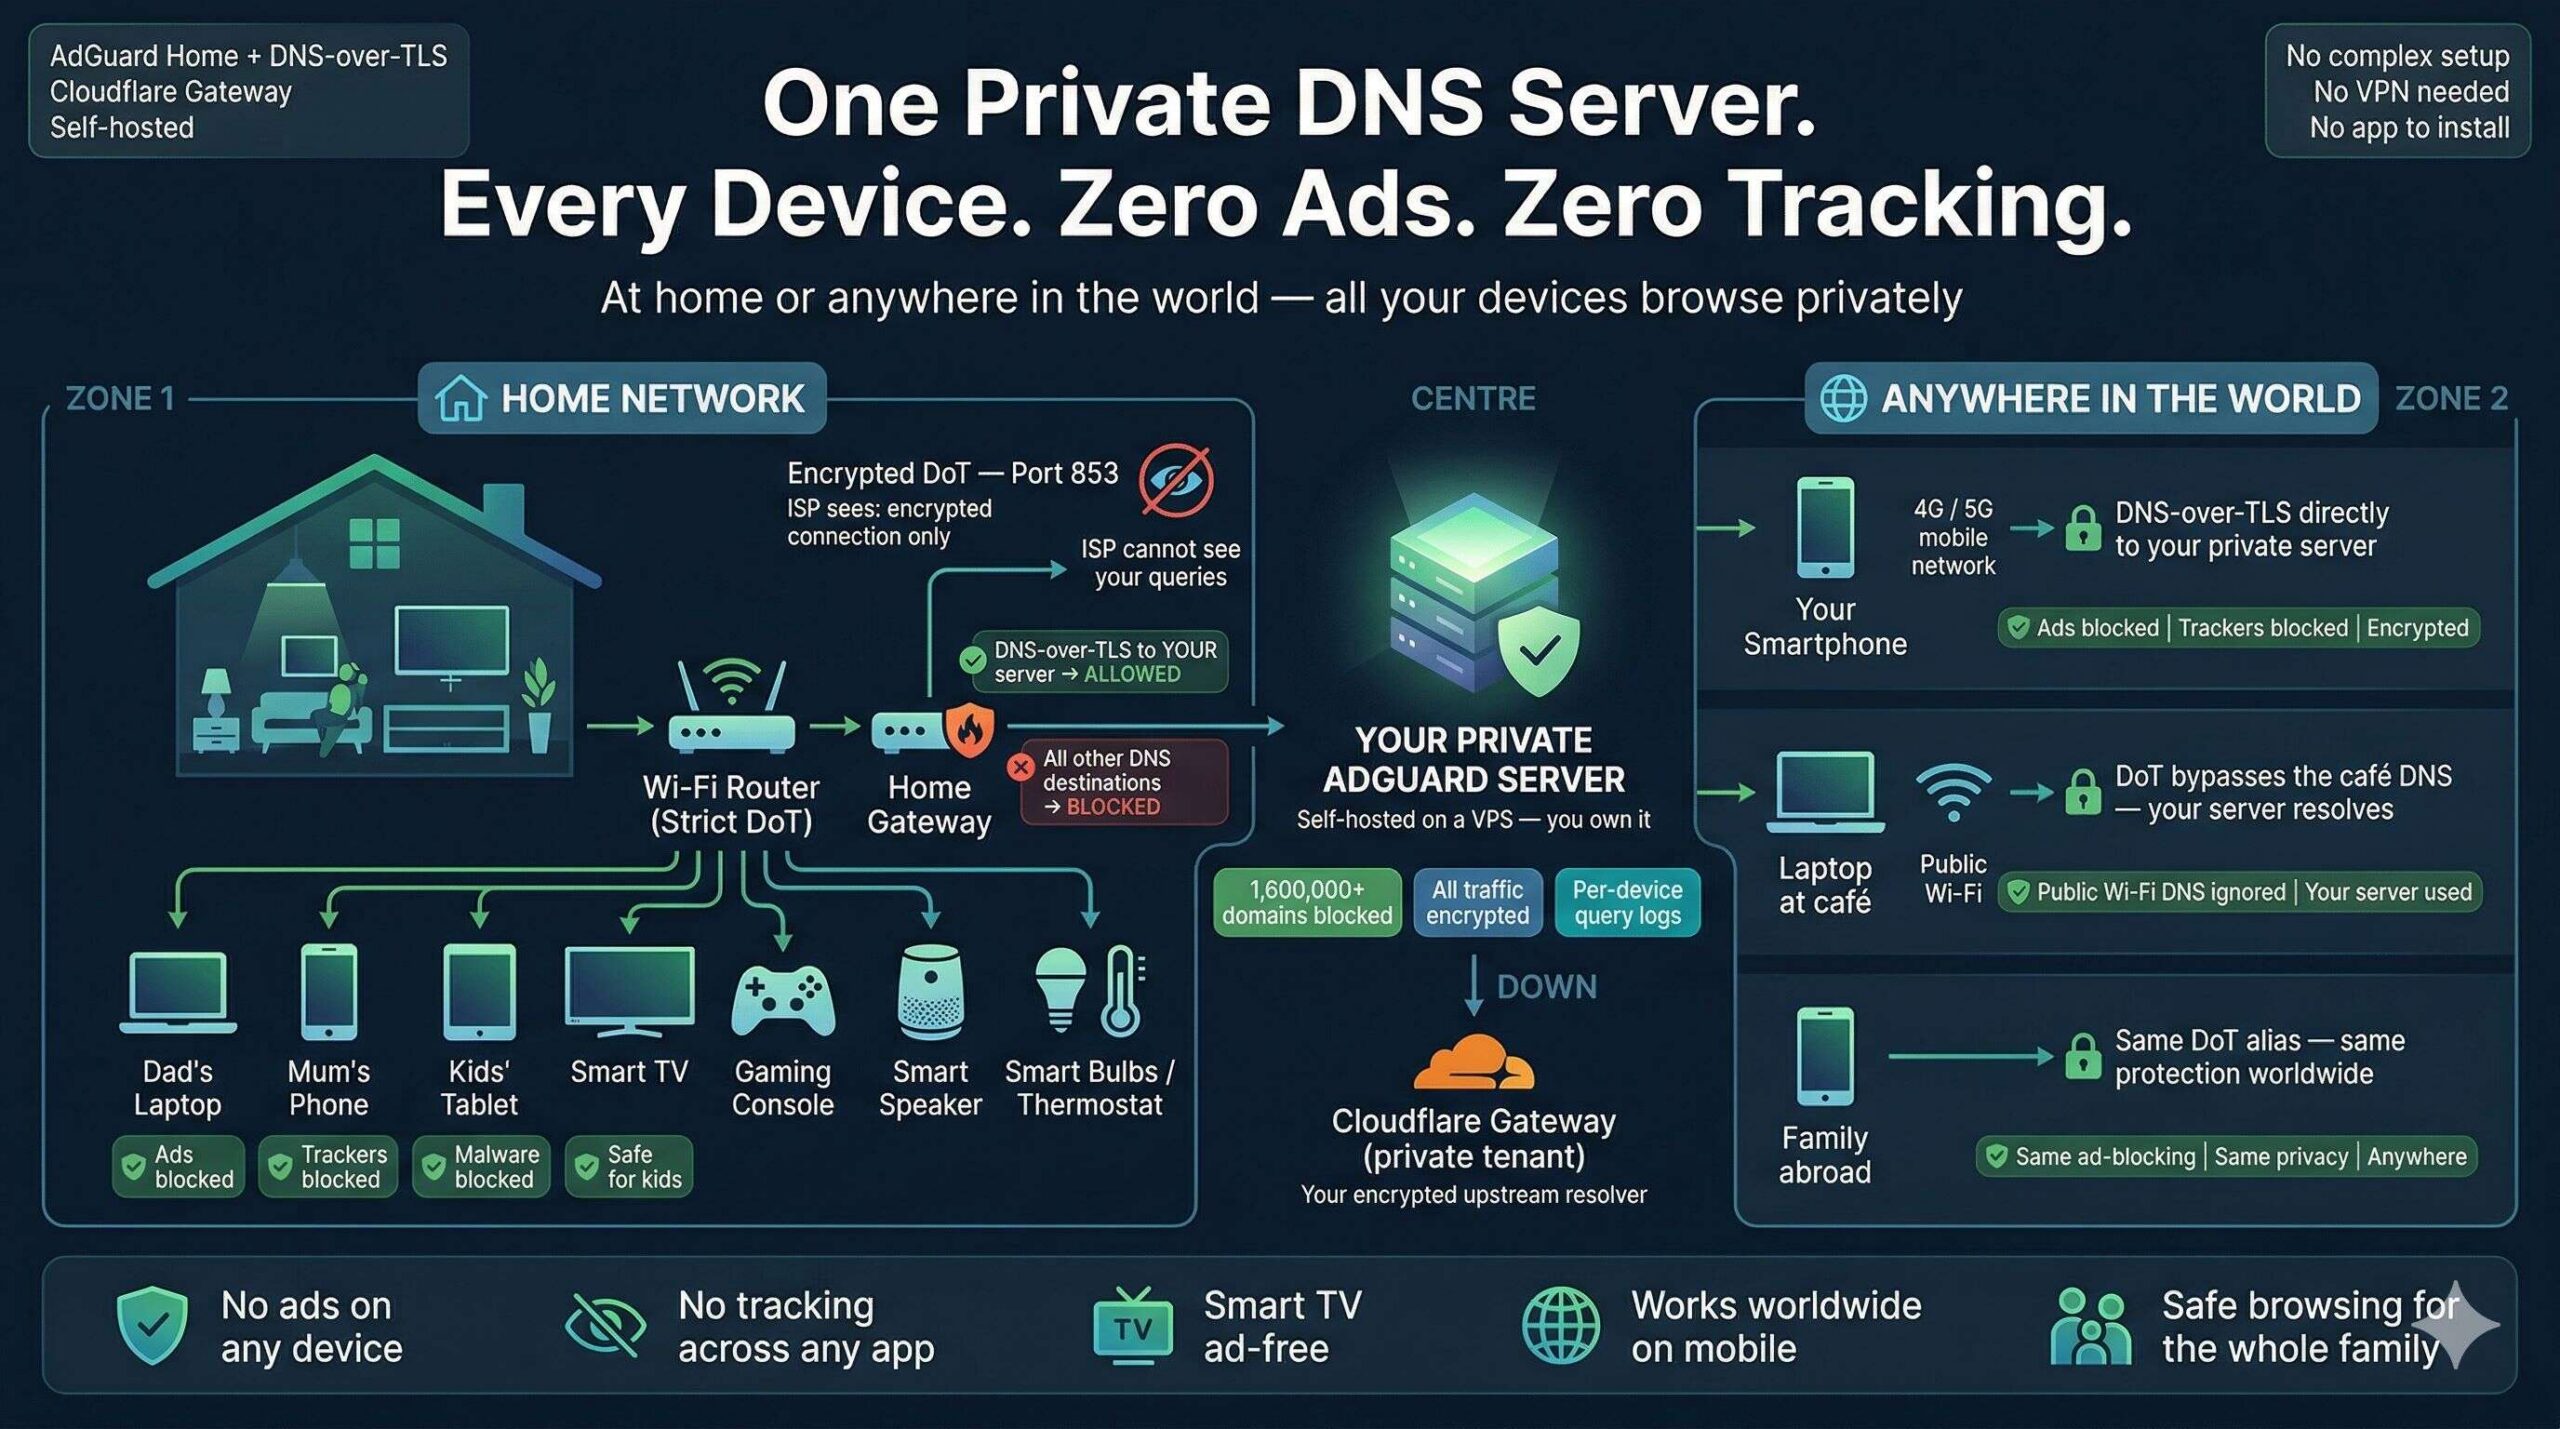
Zero Ads, Zero Tracking, Zero Exceptions: Build a Zero-Trust DNS Fortress for Every Device You Own

Zero Ads, Zero Tracking, Zero Exceptions: Build a Zero-Trust DNS Fortress for Every Device You Own

One self-hosted DNS server. Every device protected — at home and anywhere in the world. Here is a slightly terrifying, yet fun fact most people do not know: every time anyone in your household opens a browser, your Internet Service Provider (ISP) sees exactly which website they are visiting — before the page even loads. Not because they hacked your network. Not because you did anything wrong. Simply because DNS,…

Saugata Datta12 min read789
🧰

Free Tools: IP, DNS, SSL

40+ free network and other tools in one place. No signup. Click explore or visit https://technochat.in/tools

Explore